Editorial Note
This article provides practical guidance and market context. Any workflow examples, operational estimates, or financial illustrations are not AI Strategy Partners client results or a promise of performance. Linked sources support the external research cited in the article.
AI can help a service business answer routine inquiries, capture lead details, organize records, schedule a next step, and keep follow-up from depending on somebody remembering after a long day. That opportunity is real. So is the responsibility that comes with connecting an AI tool to customer conversations, business systems, and staff workflows.
The right question is not, “Is this AI safe?” No serious technology deserves a blanket yes. The useful question is, “What can this specific workflow do, what information does it need, what happens when it is uncertain, and who is accountable for the next action?” A clear answer protects the customer experience and gives the business a better way to evaluate whether the workflow is ready to launch.
Responsible AI is not a badge, a buzzword, or a promise that nothing can go wrong. It is a documented way of setting boundaries, assigning ownership, testing the real workflow, and correcting it when the business learns something new.
The Problem: AI Can Move Faster Than a Business Process
A new tool can look simple in a demo. In the real business, it may sit between a caller and the office, a web form and the CRM, an estimate and a follow-up, or a review request and a public response. That means it can affect customer expectations, staff workload, internal records, and the reputation of the business.
The cost of inaction is not only a security issue. When a business avoids the subject because it feels technical, teams often either do nothing useful with AI or experiment without a repeatable process. The first path leaves known capacity gaps untouched. The second path can create unclear ownership, inconsistent customer messages, unnecessary data exposure, and automation that staff do not trust enough to use.
A better approach is to separate four questions that are often blended together. Safety asks whether a workflow could cause harmful output or action. Privacy asks what personal or confidential information is used and whether it is needed. Security asks whether untrusted content, an attacker, or a system failure could cross a boundary. Governance asks who owns the decision, change, review, and response process. These are connected, but one does not prove another.
What Better AI Implementations Make Visible
Large platforms increasingly place trust language near their AI offers. The strongest public examples do more than say “secure” or “responsible.” They make operations visible: a testing path, an approval hold, a human escalation rule, a record of interactions, a role permission, or a clear data-use document. That is the standard a local business should expect from any implementation discussion.
There is an important distinction here. A vendor may offer human escalation, logging, encryption, or a privacy policy. That does not mean every workflow is automatically safe, private, or compliant for every business. The implementation still has to match the use case, the approved data, the operating rules, and the people who will own exceptions.
1. A bounded job—not an undefined “AI employee”
Start with a narrow business job. A voice workflow may acknowledge a routine inbound call, collect approved basic information, create a record, and notify the right team member. A follow-up workflow may send an approved acknowledgement and create a task for a human owner. The system should not be asked to diagnose a problem, make a price commitment, settle a payment dispute, decide eligibility, give legal or medical guidance, or improvise around a sensitive complaint.
2. A real human-control map
“Human in the loop” sounds reassuring, but it can mean very different things. A person may approve an action before it is sent. The system may act within a defined rule and escalate only exceptions. Or a person may review records after the fact. A responsible workflow says which of these is true, names the responsible role, and gives the team a clear pause or override path.
3. A data boundary before the tool is turned on
An AI workflow should use the minimum information needed for its job. Before a new connection is enabled, the business should be able to name the data source, approved fields, vendor or receiving system, purpose, access roles, retention setting, and deletion or disablement path. If a detail has not been verified for a specific feature, the honest answer is “to be confirmed before activation,” not a broad promise that data is never retained or never reaches a third party.
4. Permissions that match the job
A model prompt is not a security boundary. The workflow should have only the access it needs. A system that drafts a response does not need authority to change a payment method. A tool that creates a lead record does not need unrestricted access to every customer file. Where an action matters, the destination system should independently verify that the approved person or service identity is allowed to perform it.
Privacy: What Should Never Be Treated as Casual AI Input
Before teams paste, upload, or connect information to an AI feature, they should ask whether the information is necessary for the stated purpose. The safest default is to keep credentials, API keys, payment details, unnecessary customer-identifying information, private employee records, sensitive health information, confidential legal matters, and proprietary business data out of general-purpose public AI tools unless the business has reviewed the specific service, settings, and agreement that govern that use.
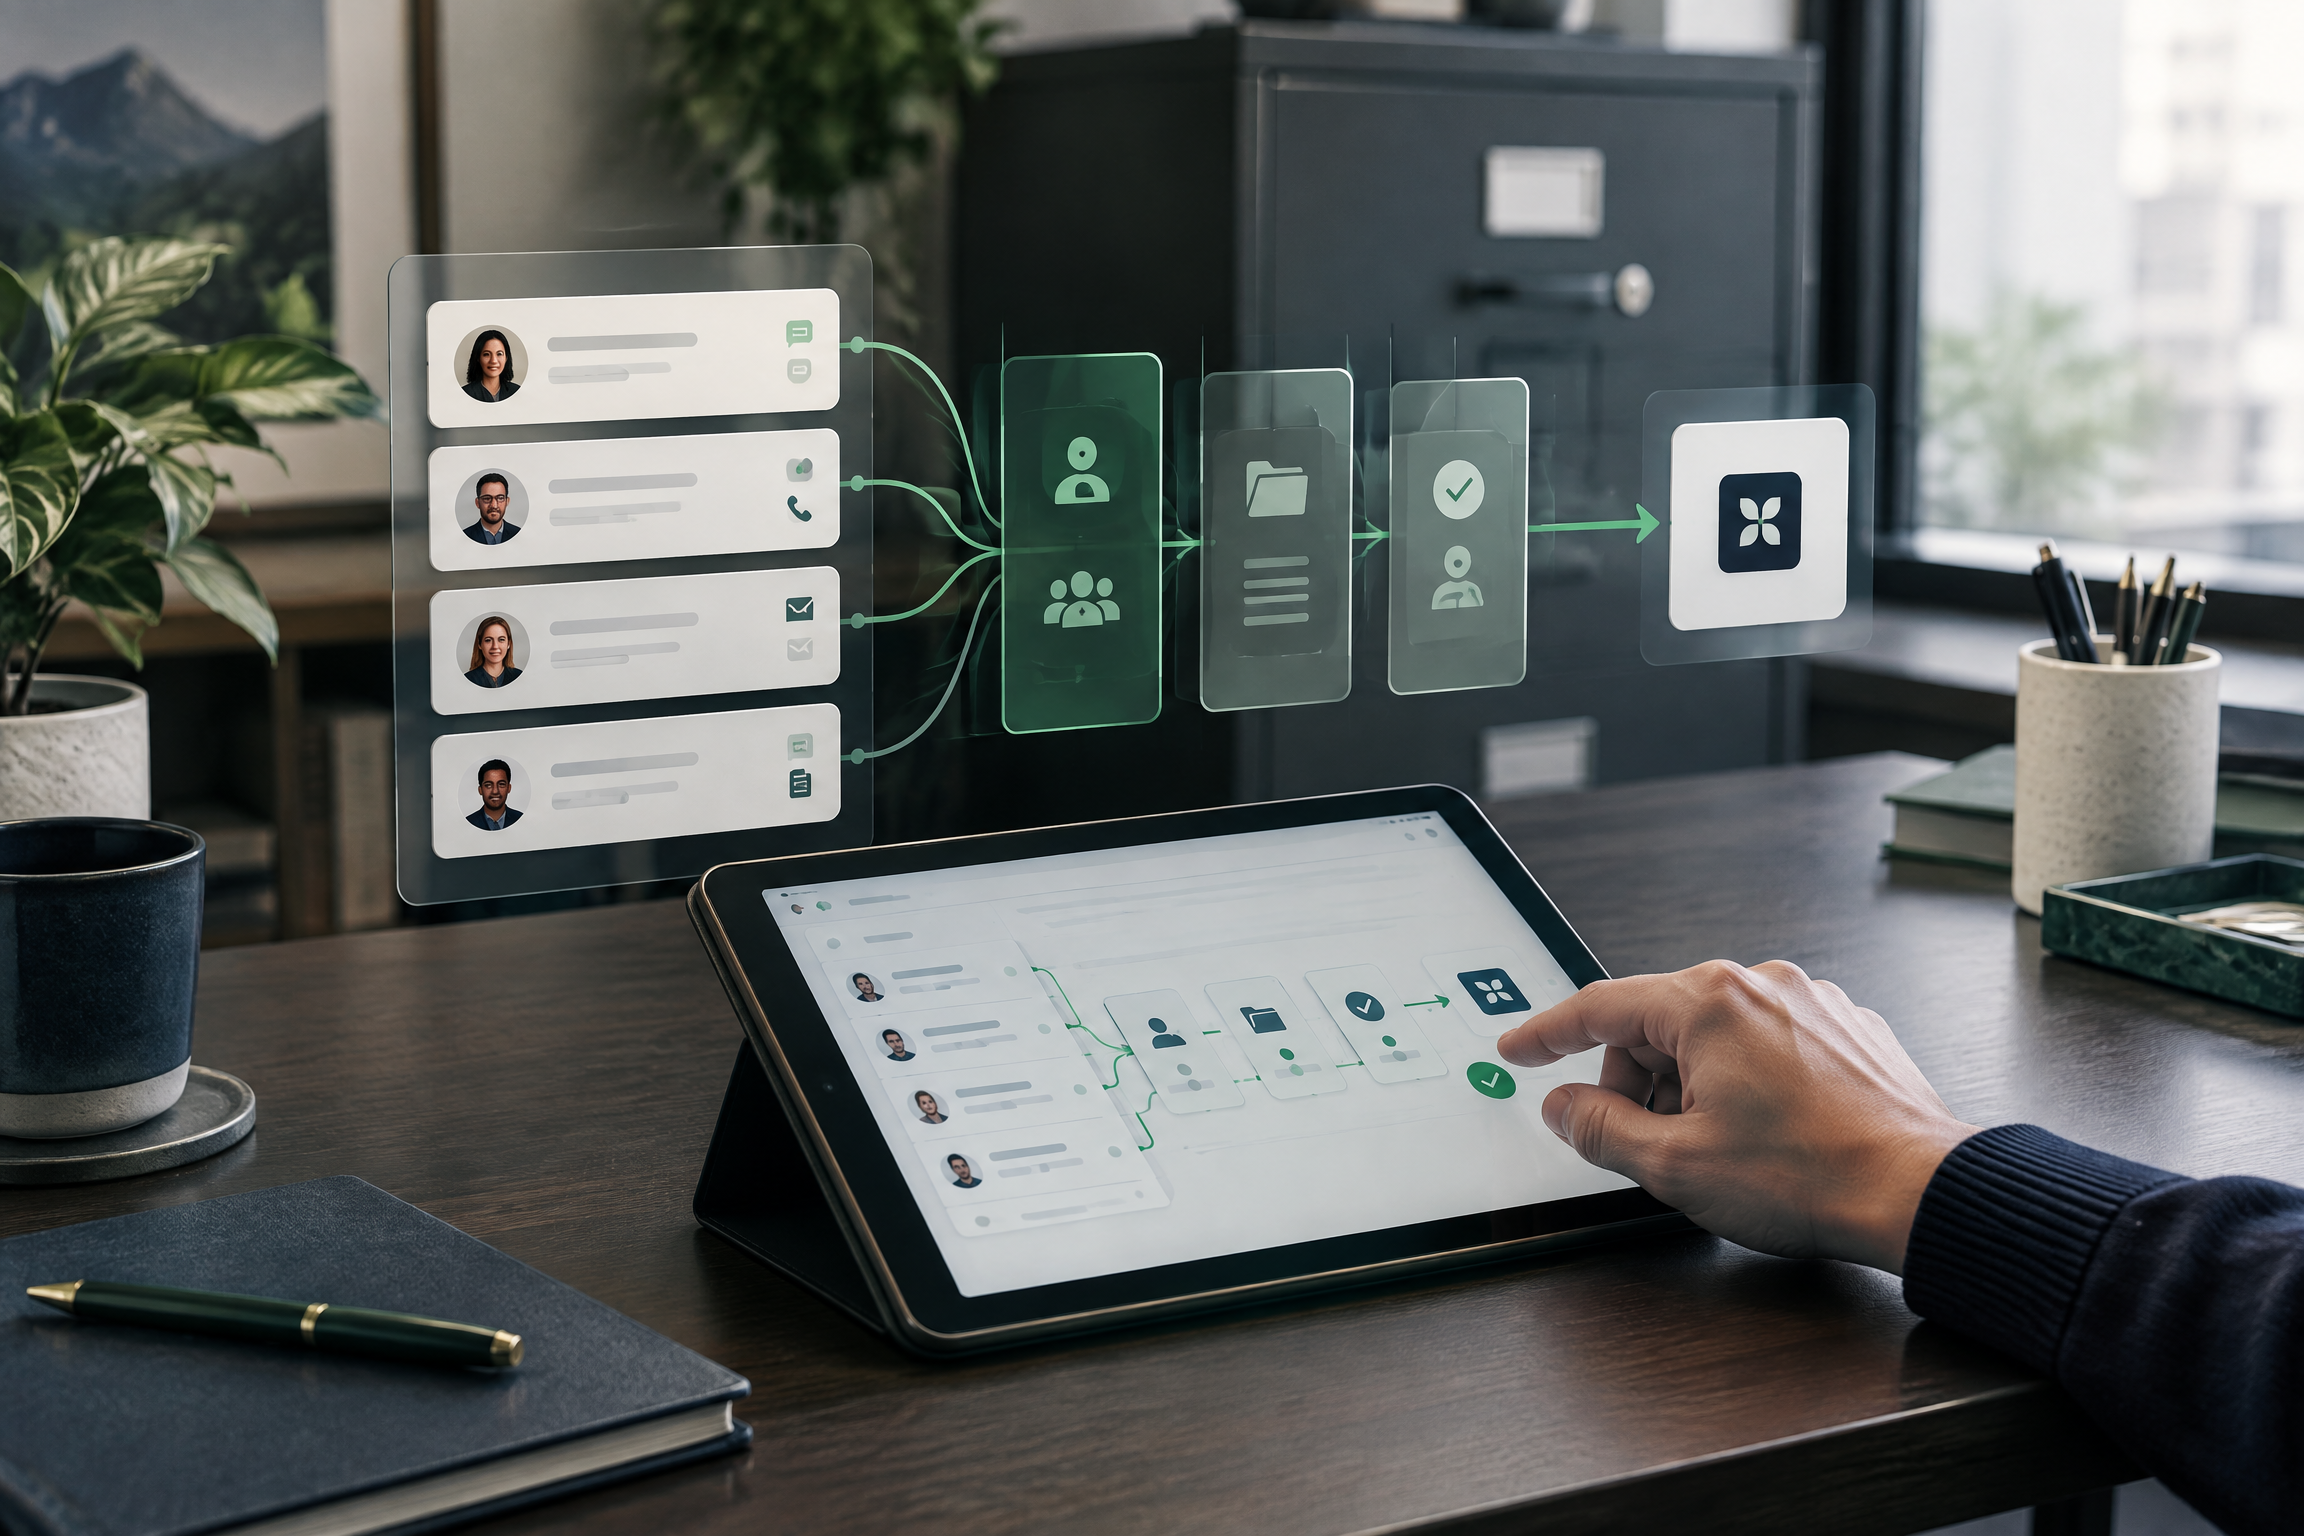
For testing and demonstrations, use synthetic or appropriately de-identified examples whenever practical. For a live workflow, decide what the system needs to do its approved job and no more. A lead-intake assistant may need a name, preferred callback method, service need, and rough location. It does not need a full account history or documents unrelated to the next step.
A privacy policy cannot rescue an unnecessary data flow. The simplest protection is to avoid collecting, sending, or retaining information the workflow does not need.
Security: Treat AI Inputs and Outputs as Potentially Untrusted
AI systems can encounter untrusted instructions in emails, web pages, uploaded files, images, forms, and retrieved documents. This is one reason an AI workflow should not have unlimited access simply because it can read a piece of content. A message can contain an instruction that is irrelevant, misleading, or intentionally designed to push the system outside its job.
The practical response is not to promise that prompts prevent every attack. It is to limit the impact. Keep model access narrow. Separate external content from business instructions. Validate outputs before they are passed into a CRM, calendar, database, browser, file system, or messaging workflow. Require human approval for higher-impact actions. Log meaningful events so the team can see what happened and correct it.
- Use unique user accounts and multi-factor authentication for systems containing customer information.
- Keep passwords, API keys, and secrets out of prompts, spreadsheets, tickets, and public files.
- Give each integration only the permissions necessary for its defined job.
- Use approved, typed actions instead of giving a model broad access to raw databases, file paths, or system commands.
- Review who can edit prompts, knowledge sources, workflows, exports, and production connections.
- Maintain a documented pause, rollback, and incident-escalation path before launch—not after the first mistake.
Implementation: A Practical Safety-First Launch Sequence
A responsible implementation does not need to become an enterprise bureaucracy. It does need a small record that makes the decision inspectable. NIST’s voluntary AI Risk Management Framework uses the lifecycle functions Govern, Map, Measure, and Manage. For a local business, that can translate into a simple, repeatable launch discipline.
- 1Define the workflow in one sentence. State the customer problem, the permitted actions, the prohibited actions, and the owner responsible for the outcome.
- 2Map the data and action path. Identify where information starts, what is sent to which system, what the workflow can create or change, and where a person approves or takes over.
- 3Set the human-control rules. Name the reviewer, escalation triggers, fallback process, pause owner, and response standard when the workflow is uncertain or unavailable.
- 4Test before go-live. Use normal, ambiguous, off-hours, privacy-sensitive, and failure scenarios. Record what passed, what did not, and what changed before launch.
- 5Launch a contained version. Start with one use case and the least risky permissions that can create useful value.
- 6Review the real record. Look at exceptions, customer feedback, staff experience, errors, unowned requests, access changes, and vendor or workflow updates. Adjust, restrict, or pause based on evidence.
The operational return on this discipline is not a promised revenue number. It is a workflow that staff can understand, inspect, and improve. That reduces rework, makes customer communication more consistent, and prevents the business from adding automation faster than it can responsibly own it.
What to Ask Before You Buy or Enable an AI Feature
- What exact routine task will this workflow perform, and what is it prohibited from doing?
- What information enters the workflow, where does it go, which vendor receives it, and what settings or agreement govern retention and use?
- Does a person approve action before it happens, receive only exceptions, or review records after the fact? Who is that person?
- What happens when the request is urgent, sensitive, unclear, outside the allowed scope, or technically unavailable?
- Which systems, fields, tools, and permissions are connected—and are they the minimum required?
- How do we test the workflow before launch, record approved changes, inspect the interaction history, and pause it if needed?
- What must the business itself decide about notices, consent, recording, retention, and legal obligations for this use case?
The AI Strategy Partners Standard: Practical, Human-Led, and Transparent
AI Strategy Partners is built for local service businesses that need systems to capture, convert, and follow up more consistently—not for businesses that want to hand customer relationships to an unchecked black box. Our implementation conversations begin with the customer path, the team’s current work, the systems already in place, and the places where human judgment must remain visible.
For an appropriate use case, the goal is to document the routine task, approved data, escalation rules, responsible owner, test scenarios, and review path before production use. We can help configure workflows around data minimization, role-based access, constrained permissions, approved messaging, human review for higher-impact steps, and a practical way to pause or correct a live process. The exact safeguards depend on the client’s systems, vendors, data, and use case.
We do not claim that a workflow is risk-free, legally compliant in every jurisdiction, immune to error, or a replacement for legal, privacy, security, or industry-specific advice. The job is more practical: make the system understandable, keep responsibility with people, and reduce avoidable risk while the business improves the work that customers experience.
Considering AI voice, CRM automation, lead follow-up, or reputation workflows? Start with a practical conversation about the customer experience, data boundaries, human handoffs, and the smallest useful pilot—not a generic software pitch.
Map a Responsible AI WorkflowFrequently Asked Questions
Is AI safe enough for a small business to use?
A small business can use AI responsibly when the use case is bounded, the data and permissions are appropriate, a person owns exceptions, and the workflow is tested and reviewed. Safety is not a one-time label. It depends on what the system is allowed to do, what information it receives, and how the business manages change and mistakes.
What is the difference between AI safety, privacy, and security?
Safety concerns harmful outputs or actions. Privacy concerns whether personal or confidential information is used appropriately. Security concerns unauthorized access, untrusted content, and system compromise. Governance assigns ownership and keeps decisions, testing, monitoring, and changes documented. A responsible deployment needs all four.
Can an AI voice agent handle every customer call?
No. A well-designed voice workflow should handle defined routine tasks and escalate situations that are urgent, safety-related, sensitive, disputed, complex, or outside the approved scope. Customers and staff should have a clear route to a person when judgment matters.
Will AI tools use our customer data to train public models?
The answer depends on the product, feature, account configuration, agreement, and data category. Do not rely on a generic promise. Before enabling a feature, review the applicable vendor documentation and document the approved fields, provider, purpose, retention settings, and any available data-use controls.
Does AI Strategy Partners make a business legally compliant?
No. Technology and workflow design can support a documented consent, notice, access, retention, and review process, but legal obligations depend on the facts, industry, agreements, and jurisdiction. Clients should obtain qualified legal, privacy, security, or industry advice for those questions.
What should a business do first before adding AI automation?
Choose one repeatable process that is important but inconsistent. Define the desired customer experience, the data that is actually needed, the human owner, the escalation triggers, and the measure that will show whether the process improved. Then test the smallest useful version before expanding.
Primary Guidance and Further Reading
The implementation guidance in this article is practical opinion. The linked primary and first-party resources provide the external context referenced above.
- NIST: Artificial Intelligence Risk Management Framework (AI RMF 1.0)
- NIST: AI Risk Management Framework and Playbook
- Federal Trade Commission: Start with Security—A Guide for Business
- Federal Trade Commission: Protecting Personal Information—A Guide for Business
- OWASP: Top 10 for Large Language Model Applications
- OWASP GenAI Security Project: Prompt Injection
- HighLevel: Privacy and Security
- ServiceTitan: AI Data Security Guidance